PHP2Shell flaws put web applications at risk; Fortinet urges patching and verification
Organisations should check PHP deployments across websites, containers and hosting providers, apply security updates and confirm that patched software is running, Fortinet advises.
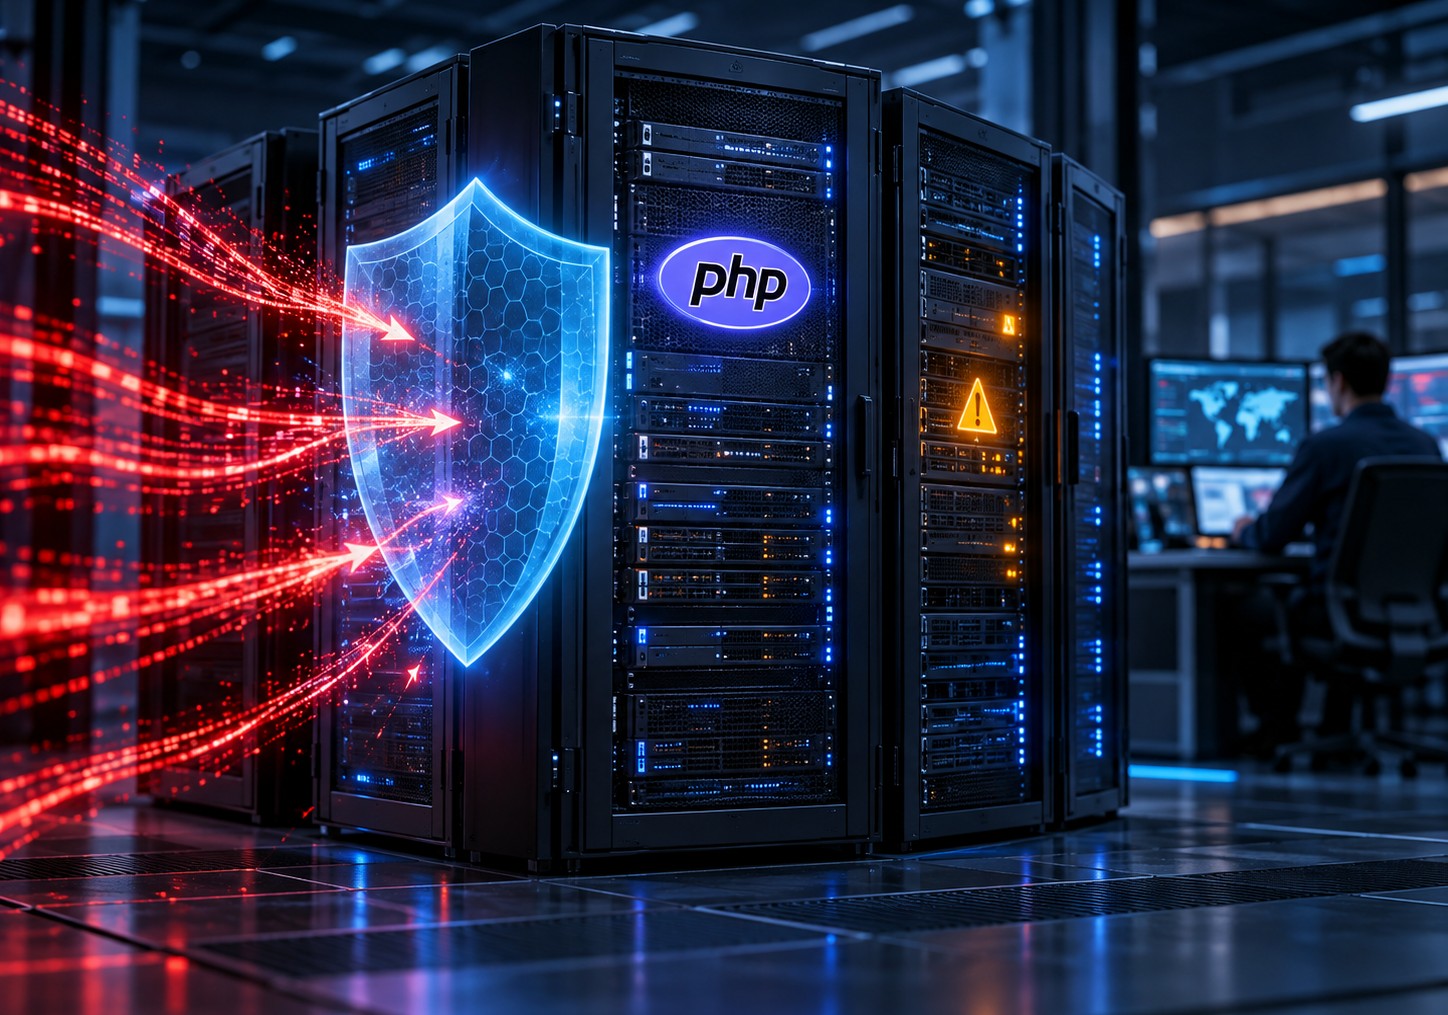
Representational image illustrating PHP web server vulnerabilities and security controls used to reduce exposure while patches are deployed.

NEW DELHI: Two critical vulnerabilities collectively known as PHP2Shell could allow attackers to execute code on affected web servers without authentication, putting business websites, customer portals and sensitive information at risk.
In a security briefing, Aamir Lakhani, Global Director of Threat Intelligence and Adversarial Artificial Intelligence Research at Fortinet, advised organisations to coordinate their security, application and infrastructure teams to deploy updates and verify that fixes are active.
The vulnerabilities, tracked as CVE-2026-109618 and CVE-2026-109619, have prompted security advisories. CERT-EU confirmed that fixes were released on October 21 in PHP versions 8.5.12, 8.4.27, 8.3.36 and 8.2.35. India’s CERT-In has also issued an advisory for MSMEs using PHP.
PHP is a server-side scripting language used by platforms including WordPress, Drupal, Joomla and Magento. Businesses may depend on it through hosting providers, commercial applications or bundled software components, even when they do not develop PHP applications themselves.
Fortinet cited an October 22 snapshot from Censys that identified approximately 36.7 million internet-facing services reporting potentially affected PHP versions. The company cautioned that these are service counts, rather than unique servers or organisations. Version-based estimates may also include installations protected through vendor-backported fixes.
The immediate task, according to the briefing, is to identify affected deployments and record their running PHP version, application owner and patch status. Reviews should include containers, managed hosting and third-party applications that bundle PHP.
Updating a software package alone does not establish that remediation is complete. Organisations should test critical workflows, deploy the appropriate runtime or vendor package, restart or replace affected workers and containers where necessary, and confirm that older processes have stopped.
While updates are being prepared, Fortinet recommends relevant intrusion prevention and web application firewall protections, tighter access restrictions and temporary isolation where exposure cannot be adequately controlled.
Its FortiGuard Labs virtual patching protections use network inspection to block known exploitation techniques before they reach vulnerable systems. Such controls can reduce exposure during deployment, but organisations still need to install and verify the underlying software fix.
Security teams should also examine suspicious web requests, unexpected PHP worker crashes, modified application files, unexplained process execution and unusual outbound connections. Where compromise is suspected, the briefing recommends preserving evidence and investigating persistence mechanisms and potentially exposed credentials.